Editorial & Technical Disclaimer: This technical analysis is based on official preliminary disclosures from Binance and independent cybersecurity research published as of October 30, 2026, while Binance’s full formal post-mortem remains underway. This article is for educational purposes and does not constitute financial advice.
Quick Summary (Verified October 30, 2026): How can an attacker drain $6.3 billion from an exchange’s hot wallets in 20 minutes without stealing its cold-storage private keys? Following the October 29, 2026 Binance attack (which began around 20:05 UTC on global Binance.com), preliminary disclosures from Binance and technical analyses from TRM Labs and security researchers revealed a two-part engineering intrusion: first, gaining access to an internal service container via a compromised DevOps engineer’s laptop (alongside additional breach points uncovered in ongoing investigations); and second, leveraging transaction-signing manipulation—including Ethereum’s EIP-7702 account-abstraction delegation—to sweep hot wallets. Note that 100% of customer balances are covered by Binance’s SAFU and corporate reserves, ~$3 billion has been frozen on-chain, and Binance.US was completely unaffected.
1. Timeline of the October 29–30, 2026 Binance Attack
Based on verified on-chain timestamps and Binance’s official announcements:
- October 29, 2026 (20:05 UTC): Unauthorized withdrawal transactions begin executing from
Binance.comhot wallets across 10 to 11 blockchains (including Ethereum, Bitcoin, Solana, BNB Chain, and XRP Ledger). - October 29, 2026 (20:05 – 20:35 UTC): Approximately $6.3 billion in digital assets is moved out within a 20-to-30-minute window before automated and manual containment halts further outflows.
- October 29–30, 2026 (Containment & On-Chain Freeze): Binance suspends withdrawals, revokes affected address authorizations, and coordinates with Tether, Circle, and blockchain security councils to freeze approximately $3 billion on-chain.
- October 30, 2026 (Official Updates #1 & #2): Binance publishes its preliminary findings, confirms zero user losses, and sets aside over $6.34 billion in corporate and SAFU funds (including $5 billion in the exact impacted tokens) to back customer balances 1:1.
2. Stage 1: Compromised DevOps Laptop and Internal Service Container Access
In its initial October 30, 2026 disclosure, Binance stated:
“Binance’s initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak.”
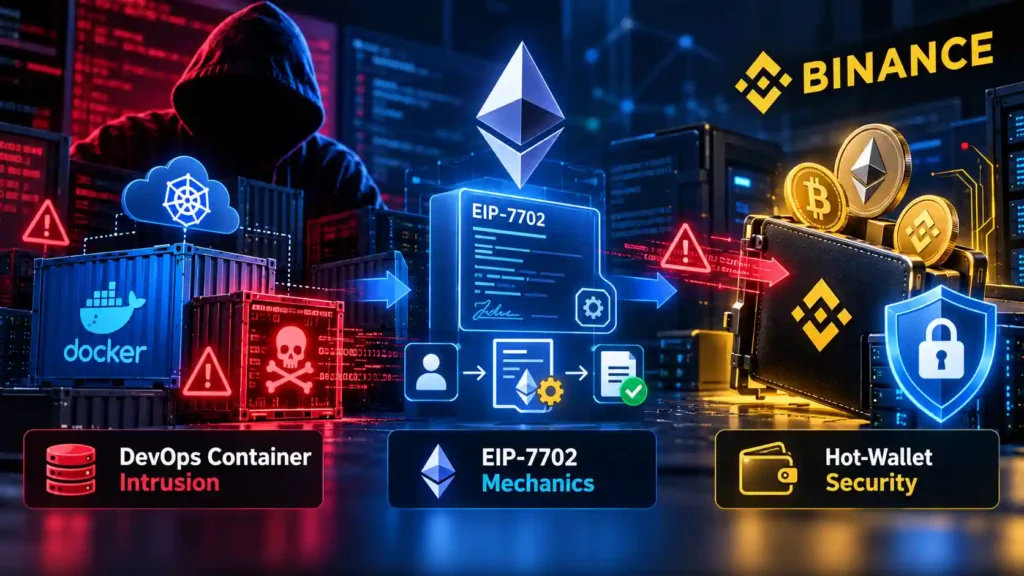
In modern cryptocurrency exchange architecture, private keys for hot wallets (wallets connected to automated settlement pipelines to fulfill instant user withdrawals) are typically stored inside Hardware Security Modules (HSMs) or Multi-Party Computation (MPC) enclaves. Employees cannot simply view or copy a raw private key text file. Instead, internal microservices running inside containerized environments (such as Kubernetes pods or Docker service containers) send authenticated signing requests to the enclave after verifying business logic.
When an advanced threat actor—attributed by TRM Labs and Cybersecurity Dive to North Korea’s TraderTraitor—compromised the DevOps engineer’s endpoint and pivoted into internal service containers, they did not need to extract the underlying cryptographic key material. Instead, they gained the ability to feed unauthorized transaction requests into the signing pipeline from a trusted internal service context.
3. Stage 2: How EIP-7702 Delegation Was Abused on Ethereum Hot Wallets
Why didn’t the attacker just submit thousands of individual token transfer requests, which might have triggered rate limits or anomaly detection? On Ethereum, blockchain security researchers observed that the attacker leveraged EIP-7702, an Ethereum Improvement Proposal introduced in the Pectra upgrade:
- What EIP-7702 Was Designed to Do: Normally, an Ethereum wallet is either an Externally Owned Account (EOA) controlled by a private key, or a Smart Contract Wallet controlled by code. EIP-7702 allows a standard EOA to sign a special authorization tuple (
SET_CODE_TX_TYPE/ transaction type0x04) that delegates its execution logic to a smart-contract address—giving regular wallets smart-contract features like transaction batching. - How Attackers Abused It in the Binance Attack: By inducing the compromised internal container/signing pipeline to authorize an EIP-7702 delegation pointing to an attacker-controlled “sweeper” smart contract, the hot wallet’s EOA temporarily adopted the attacker’s malicious contract code. That allowed the attacker to batch-sweep multiple ERC-20 tokens and native ETH in rapid succession before authorizations were revoked.
4. Why “No Private Key Leak” Matters (Hot Wallets vs. Cold Storage)
To understand why Binance was able to contain the breach and guarantee 100% of user funds, it helps to compare the three tiers of exchange wallet architecture:
| Wallet Tier | Purpose & Connectivity | Status in the October 2026 Binance Attack |
|---|---|---|
| Cold Storage Wallets | Holds the vast majority of exchange reserves completely offline (air-gapped hardware/multi-signature vaults). | Untouched. Cold storage keys were never exposed or accessed. |
| Hot Wallets (HSM / MPC) | Internet-connected operational buffers holding liquidity for immediate customer withdrawals. | Impacted via unauthorized service-container transactions (~$6.3B); no raw private keys leaked; authorizations revoked and ~$3B frozen on-chain. |
| SAFU & Corporate Treasury | Emergency insurance reserve (Secure Asset Fund for Users) + company balance sheet. | Deployed ($6.34B+ set aside) to cover 100% of un-recovered hot-wallet outflows so customer balances remain intact. |
5. Engineering & User Security Lessons From the Binance Attack
The October 2026 Binance attack carries critical takeaways for both enterprise DevSecOps teams and individual cryptocurrency holders:
- Harden Developer Laptops & Prevent Secret Leaks: Because a single compromised developer laptop can become an entry point into production containers, engineering teams must enforce strict endpoint isolation, zero-trust container policies, and pre-commit secret scanning—see our guide on protecting private Git repositories and developer environments from secret leaks.
- Explicitly Filter EIP-7702 Type
0x04Authorizations in Signing Policies: Institutional custody engines and hardware wallets must treat EIP-7702authorization_listpayloads with the same multi-quorum human approval required for master smart-contract upgrades. - Protect Your Personal Account From Post-Breach Phishing: Individual users on
Binance.comandBinance.USshould immediately enable hardware-backed FIDO2 passkeys (see our tutorial on how to use passkeys on Windows 11), configure their custom Anti-Phishing Code, and review our full Binance Account Protection & Incident Response Guide.
6. Frequently Asked Questions (FAQ)
How did the October 2026 Binance attack happen?
According to Binance’s preliminary findings on October 30, 2026, the attack involved a compromised DevOps engineer’s laptop (along with additional breach points under investigation) that allowed an attacker to access an internal service container and submit unauthorized withdrawal transactions from platform hot wallets across 10–11 blockchains.
Were Binance’s private keys leaked during the attack?
No. Binance confirmed that its investigation found no evidence of any wallet private key leak. Instead, the attacker abused internal service-container access and transaction-signing mechanisms (including Ethereum EIP-7702 delegation) to trigger unauthorized withdrawals.
What is EIP-7702 and how was it used in the Binance attack?
EIP-7702 is an Ethereum upgrade feature that allows a standard wallet (Externally Owned Account) to delegate its execution logic to a smart contract. In the October 2026 attack, the attacker got the compromised signing pipeline to authorize an EIP-7702 delegation to a malicious sweeper contract, rapidly draining multiple tokens from the Ethereum hot wallet.
Are customer funds safe after the Binance attack?
Yes. Roughly $3 billion of the stolen assets were frozen on-chain within hours, and Binance set aside over $6.34 billion from its SAFU fund and corporate reserves to cover 100% of the losses. Additionally, Binance.US confirmed its separate US platform was not affected.