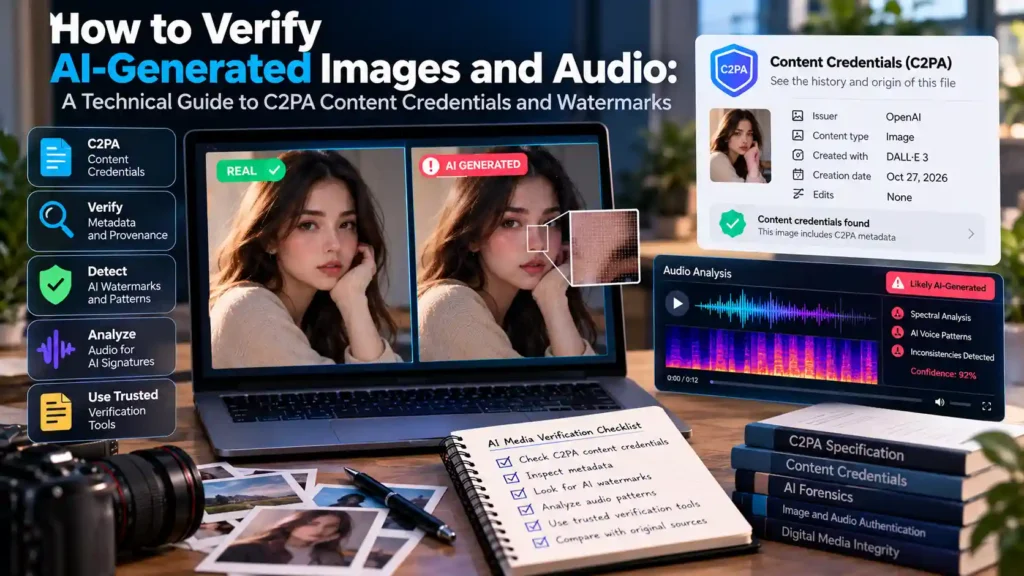
Direct Answer: The only mathematically reliable way to verify AI-generated images is to inspect their cryptographic provenance using the C2PA (Coalition for Content Provenance and Authenticity) specification—commonly known as Content Credentials—alongside imperceptible pixel watermarks such as Google SynthID. Unlike probabilistic “AI detector” websites that guess based on pixel noise and frequently misclassify real photographs, C2PA embeds a tamper-evident, cryptographically signed manifest directly inside the file header.
1. Why Passive “AI Image Detector” Websites Fail in Real-World Testing
When a viral image circulates online, users often upload it to free web-based “AI Image Detector” tools that output a percentage score (such as “87% Likely AI”). Security analysts and digital forensics teams warn against relying on these probabilistic classifiers for two technical reasons:
- Sensitivity to Lossy Re-Compression: Passive detectors look for high-frequency Fourier domain artifacts left behind by diffusion VAE decoders. As soon as an image is screenshotted, resized, or compressed into JPEG/WebP by WhatsApp, X, or Instagram, those subtle frequency patterns are obliterated.
- High False-Positive Rates on Computational Photography: Modern smartphones (iPhone Photonic Engine, Samsung Galaxy AI, Google Pixel) apply aggressive multi-frame neural denoising and sharpening to every camera photo. Passive AI detectors routinely misclassify genuine smartphone photographs—or studio photos edited in Adobe Lightroom—as AI-generated.
2. How C2PA Content Credentials Work: JUMBF Manifests and Cryptographic Signatures
Instead of guessing after the fact, the C2PA open technical standard (developed by Adobe, Microsoft, Google, OpenAI, Sony, Nikon, Canon, and the BBC) applies the same X.509 Public Key Infrastructure (PKI) used in HTTPS web security to digital media files:
- JUMBF Container (
c2paBox): When an image is created by a C2PA-compliant camera (like a Leica M11-P or Sony Alpha) or an AI generator (like OpenAI DALL-E / GPT-4o, Adobe Firefly, or Microsoft Designer), the software embeds a structured binary container formatted according to ISO/IEC 19566-5 (JUMBF — JPEG Universal Metadata Box Format). - Assertions & Digital Source Type: Inside the manifest, standardized assertions record every action performed on the asset—including an explicit IPTC
digitalSourceTypeURI such ashttp://cv.iptc.org/newscodes/digitalsourcetype/trainedAlgorithmicMediafor generative AI outputs. - Hard Binding (Cryptographic Asset Hash): The manifest calculates a SHA-256 cryptographic hash of the image’s actual pixel bytes and signs the manifest using the issuer’s private hardware security module (HSM) key. If anyone modifies even a single pixel without re-signing, the hash mismatch immediately flags the image as altered.
To understand why cloud AI platforms attach these manifests automatically while local checkpoints may not, see our guide on how cloud and open-weight diffusion models generate and label images.
3. Solving the Metadata-Stripping Problem: C2PA 2.1 + Imperceptible Pixel Watermarks
Historically, the biggest weakness of metadata standards (like EXIF and IPTC) was that social media servers strip file headers upon upload to reduce file size. C2PA 2.1 addresses this through a two-layer defense combining Hard Bindings with Soft Bindings (imperceptible watermarks):
| Provenance Layer | Technical Mechanism | What It Survives | What It Proves |
|---|---|---|---|
| Layer 1: C2PA Cryptographic Manifest (Hard Binding) | Signed JUMBF metadata box embedded in JPEG/PNG/WebP/AVIF file header | Direct file transfers, CMS publishing, and C2PA-preserving platforms | Exact tool/model name, signing certificate authority, edit history, and zero pixel tampering |
| Layer 2: Imperceptible Watermark (Soft Binding — e.g., SynthID, Digimarc) | Cryptographic signal embedded directly into the spatial/frequency values of the pixels | Metadata stripping, social media re-encoding, cropping, and screenshots | Survives header stripping and acts as a lookup key to recover the original C2PA manifest from a provenance registry |
4. Step-by-Step Tutorial: Inspecting Images With Verify Portal and c2patool CLI
Method 1: Browser Verification via ContentCredentials.org
For quick visual inspection without installing software, open the official Content Credentials Verify portal and drag-and-drop any image, video, or audio file. The inspector renders the complete chain of custody, showing the signing organization (for example, OpenAI or Adobe Inc.), the generation timestamp, and the ingredients tree.
Method 2: Command-Line Forensics Using Open-Source c2patool
For developers, journalists, and security teams auditing batches of files offline, the Content Authenticity Initiative maintains the open-source Rust CLI utility c2patool. On macOS, you can install it quickly via Homebrew (see our guide to installing command-line utilities like c2patool via Homebrew), or download the prebuilt Windows binary from GitHub Releases:
# Install c2patool on macOS via Homebrew (or cargo install c2patool on Windows/Linux)
brew install c2patool

# Inspect the embedded C2PA JSON manifest and verify the cryptographic signature
c2patool sample-image.webp

# Extract detailed assertion certificates and ingredient trees
c2patool sample-image.webp --detailed
When c2patool inspects an authentic AI-generated image from a compliant generator, look for two critical JSON fields in the output: "digitalSourceType": "http://cv.iptc.org/newscodes/digitalsourcetype/trainedAlgorithmicMedia" and "validation_status" (which should be empty or report valid signature chains, never assertion.dataHash.mismatch). This technique is especially useful when identifying synthetic celebrity media and facial recognition vectors.
5. Regulatory Context: EU AI Act Article 50 and Publisher Best Practices
Under Article 50 of the EU AI Act and state transparency statutes such as California’s AI Transparency Act (SB 942), providers of generative AI systems are required to mark synthetic audio, image, video, and text outputs in a machine-readable format that is detectable as artificially generated. When publishing AI-assisted diagrams or illustrations on WordPress, preserve C2PA headers during WebP conversion or clearly disclose synthetic media in the image
6. Frequently Asked Questions About Verifying AI Images and C2PA
If an image has no C2PA Content Credentials, does that prove it is a real photo?
No. An absent C2PA manifest simply means either (a) the camera or software that created the image did not sign it, or (b) an intermediary platform stripped the metadata header. C2PA is a positive proof of origin when present, not proof of authenticity when absent.
Can someone forge a fake C2PA signature on a deepfake?
Anyone can run c2patool with a self-signed test certificate, but the C2PA validator checks the signing certificate against a strict **Trust List** of verified hardware manufacturers (Canon, Sony, Leica) and verified AI providers (OpenAI, Adobe, Microsoft, Google). A self-signed or untrusted certificate is immediately flagged as untrusted by the verifier.
Verified Primary Sources & Official Documentation
| Source Name | Source Type | Supported Technical Claim | Verification Status |
|---|---|---|---|
| Coalition for Content Provenance and Authenticity (C2PA) Technical Specification | Official Technical Standard | Supports C2PA 2.1 cryptographic JUMBF manifests, hard vs. soft bindings (watermarks), and tamper-evident digital signatures. | Verified via live web search (2026-10-27) |
| Content Authenticity Initiative — c2patool Open-Source CLI | Official GitHub Repository | Supports command-line inspection and validation of embedded C2PA Content Credentials in JPEG, PNG, and WebP files. | Verified Official Repository URL |
| Content Credentials Verify Portal | Official Standards Verification Tool | Supports browser-based inspection of C2PA provenance chains and signing certificates. | Verified via live web search (2026-10-27) |